That is so cool! https://twitter.com/donnaeilidhkean/status/1529797165387857921
(original)
That is so cool! https://twitter.com/donnaeilidhkean/status/1529797165387857921
(original)
RT @CarymaRules: Lawyer with confirmed RSVP to Doug Ford rally denied entry for dissenting views, arrested for trespass upon asking questio…
(original)
RT @ZackBornstein: Guns are banned at Trump’s speech at the NRA convention tomorrow bc they know that’s the only way to prevent a shooting
(original)
RT @steve_vladeck: I look forward to hearing the same folks who have been insisting that teachers just can’t be trusted to decide how/what…
(original)
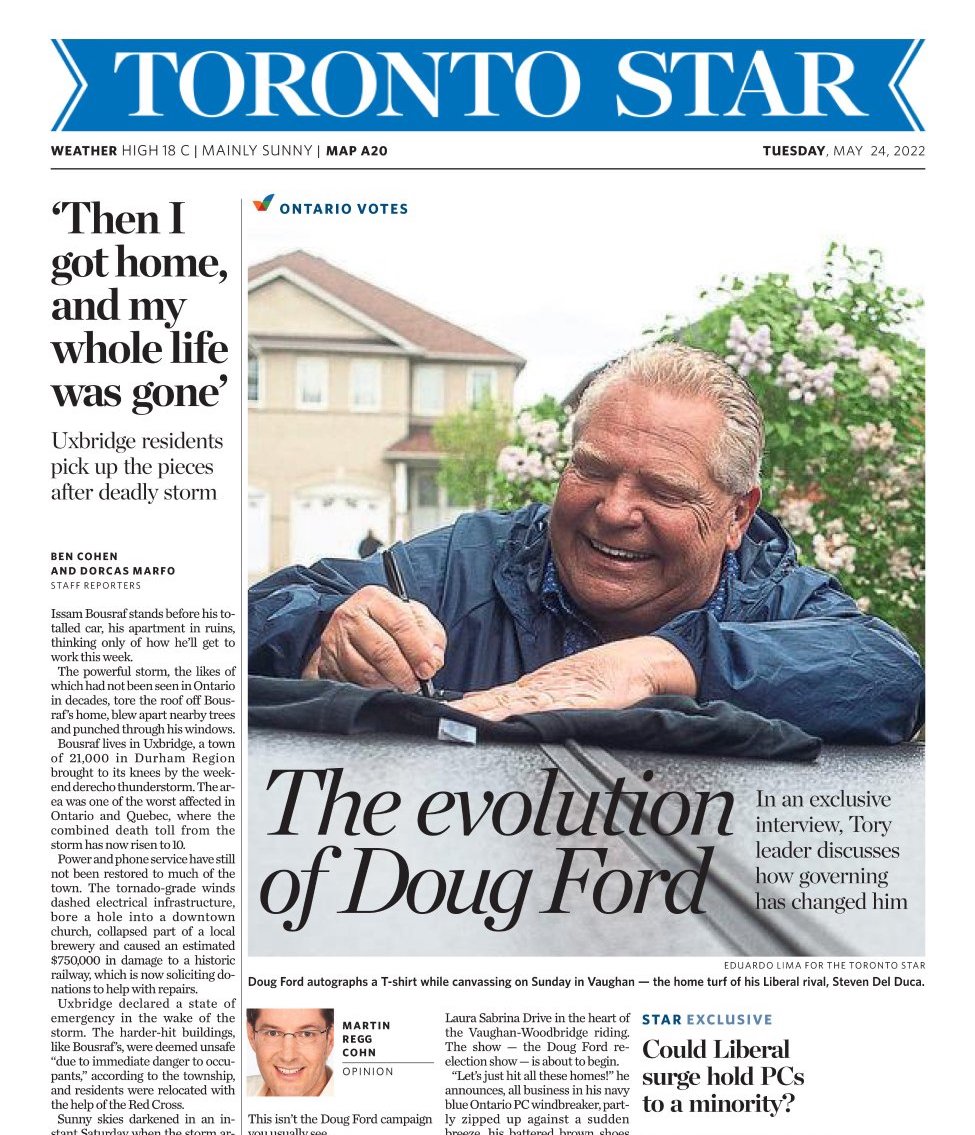
RT @TheBeaverton: Toronto Star proudly announces new job as official Ford Campaign PR firm #onpoli #NewsInPhoto
(original)
RT @TheBeaverton: Republicans relieved no fetuses killed in Texas school shooting https://www.thebeaverton.com/2022/05/republicans-relieved-no-fetuses-killed-in-texas-school-shooting/
(original)
RT @ChrChristensen: 26 years ago, a gunman entered Dunblane Primary School in Scotland, killing 16 kids and a teacher. The UK govt responde…
(original)
Hoping for this again this year 🤞🏼 #WWDC22 https://twitter.com/mruncieman/status/1400652649620545536
(original)
RT @parentaction4ed: Every time the going got tough, Ford hid. He’s hiding now. Lecce was the same (graphic from Jan/22 when they shut scho…
(original)
RT @trishanmo: “He’s just an asshole.”
Memories from 2014 when John Oliver talked about Doug Ford running for mayor of TO. Instead we ele…
(original)
RT @brittlestar: WHY THE ONTARIO PC’S ARE GOING TO WIN THE ELECTION
(original)
RT @parentaction4ed: Lecce & Ford really took one look at what our kids need after 2.5 years of pandemic and said:
“We’re going to cut fr…
(original)
I’d rather pay for my plate sticker… https://twitter.com/WendyGoodes/status/1528022767915999232
(original)

RT @Eugene_Scott: Laws restricting lessons on racism are making it hard for teachers to discuss the massacre in Buffalo https://t.co/MDq8Xd…
(original)
Not ideal to say the least. Apparently one of the only ways to stop getting these messages entirely is to turn off RCS. https://apple.news/AjDwrfHSQSUKBhTt8R-DYQg
(original)
Savathun mask details are finished and all thats left is to paint it! Also had a lot of requests for voice lines <3 #destiny2 #ad #thewitchqueen @DestinyGameUK @DestinyTheGame pic.twitter.com/Dx23KMpwLd
— Willow Creative (@WillowCreativ) May 20, 2022
RT @atrupar: Tucker Carlson tries to distance himself and Fox News from the Buffalo shooter, who was inspired by racist conspiracy theories…
(original)
RT @mmasnick: So, it’s quite likely that Twitch removing this channel violates Texas’ new social media content moderation law, which is now…
(original)